Executive Summary: A cachedData integration needs more than one incomplete-response fixture and one successful live result. The field is optional, arrives inside an asynchronous request, can be absent, can carry a match that differs from live, and can reach downstream systems more than once through polling or callback behavior. A release-ready test plan should prove state invariants across every branch while keeping interim provenance and finality intact.
What Contract Should the Tests Treat as Authoritative?
Which behavior comes from Cobalt?
Use the approved feature brief for the new interim field: an incomplete long-running response may include cachedData, its record can include updatedAt, the live search continues under the existing request, the field may be absent, cached and live matches may differ, and the completed live result remains final.
Use Cobalt's public SOS reference for the baseline request and response contract,[1] and its Help Center for incomplete status behavior.[2]
Which behavior belongs to the customer?
Mocks, fixtures, age thresholds, match policy, permitted interim actions, idempotency keys, review rules, logging, and release criteria belong to the integrator. Do not invent an undocumented provider test flag or state guaranteed to return a particular cached fixture.
Test the documented contract, then test every customer-owned interpretation separately.
Label synthetic fixtures clearly and keep them out of production evidence.
Pin every test to source and retrieval metadata. The approved feature brief can be hashed and stored with the test-plan version, while public documentation URLs and retrieval dates support baseline behavior. If the contract changes, reviewers can see which tests were derived from which version instead of updating fixtures without an evidence trail.
Which State Model Should the Test Plan Prove?
What are the minimum process states?
A practical model includes accepted, live pending without cache, live pending with cache, interim allowed or withheld, live complete match, live complete no-match, review required, and terminal error. Cobalt's status guide distinguishes incomplete, completed, no-results, cache-related, and failure meanings.[3]
The customer's exact names may differ. The test contract should specify allowed transitions rather than infer them from populated fields.
Which invariants must always hold?
• Pending stays non-final. cachedData never marks live verification complete.
• Absence stays neutral. Missing cachedData never becomes final no-match.
• Source stays explicit. Cached and live observations never exchange labels.
• History stays immutable. Final data does not erase an interim observation that was used.
• Terminal state is monotonic. A late event cannot return completion to pending.
• Effects are idempotent. Repeated delivery produces at most one effect per purpose.
• Artifacts keep parentage. A live screenshot never attaches to the cached observation.
Write each invariant as an automated negative assertion, not only as expected happy-path output.
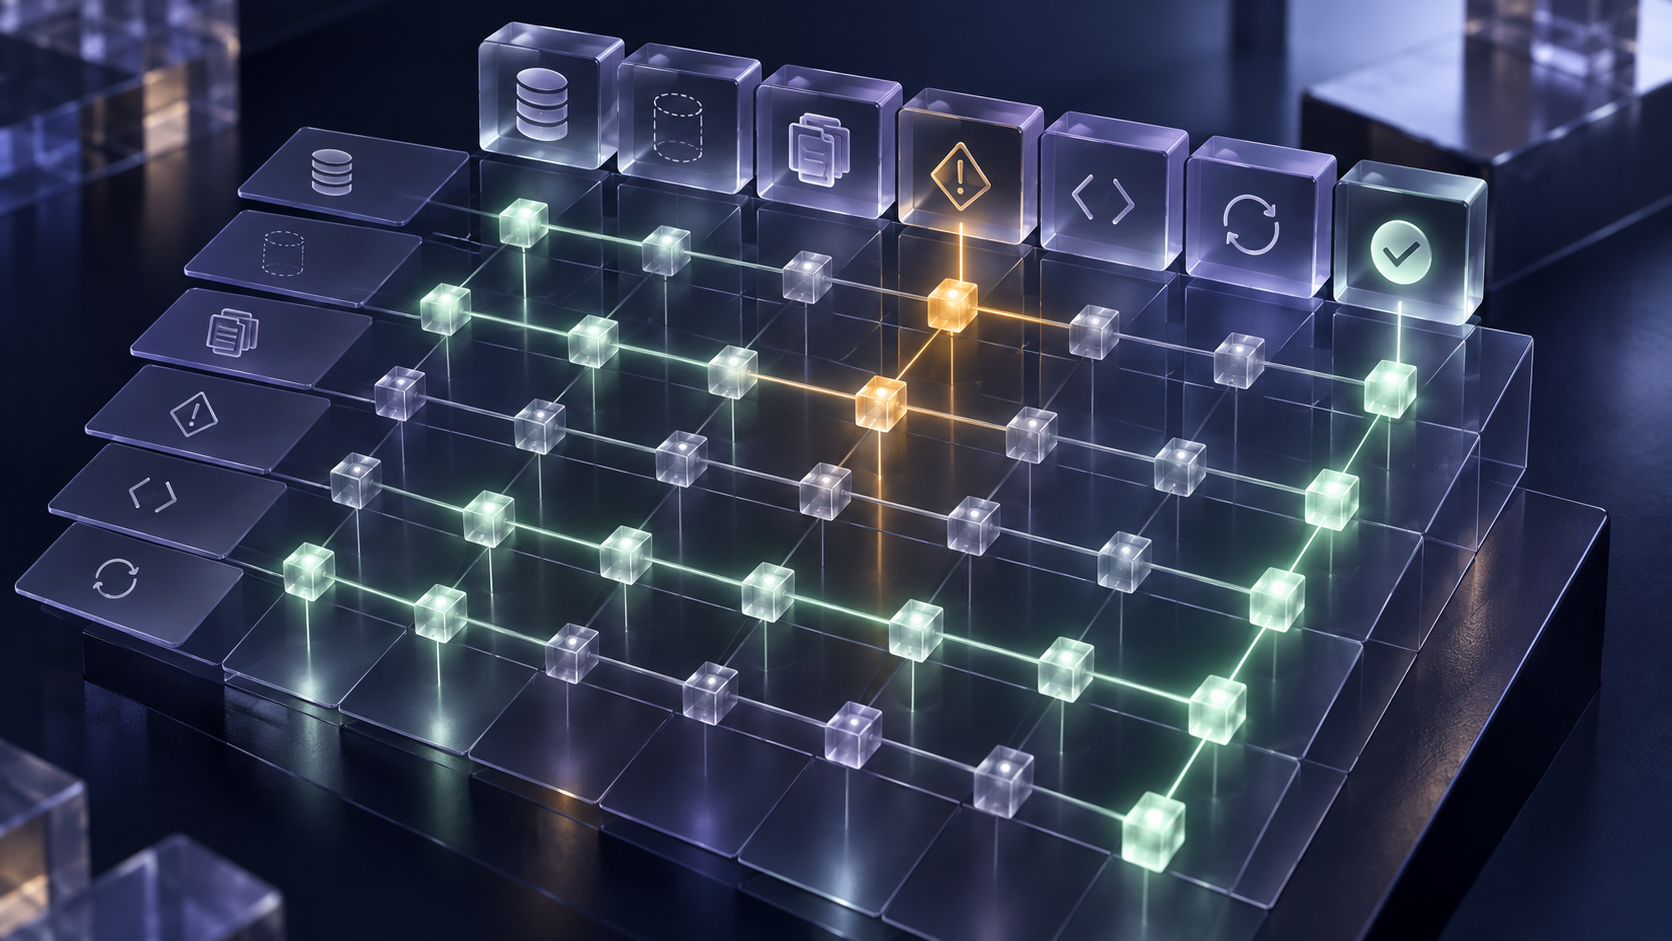
Create a transition table that names current state, input event, validation, next state, observations written, and effects permitted. Generate parameterized tests from the table where practical, then add hand-written race and failure cases. The table becomes an executable contract between the API adapter, orchestration service, user interface, and downstream consumers.
Which Fixtures Cover Cache Presence and Absence?
What should the cache-present fixture contain?
Include 202, Incomplete, a valid retryId, and one cachedData record with title, status, normalized status, registration state, and updatedAt. Preserve only documented feature fields and values plausible for the test. Add customer receipt time in the test runner, not in the provider payload.
{
  "status": "Incomplete",
  "statusCode": 202,
  "retryId": "test-retry-id",
  "cachedData": [{
    "title": "EXAMPLE COMPANY LLC",
    "status": "Active",
    "normalizedStatus": "Active",
    "stateOfSosRegistration": "CA",
    "updatedAt": 1788994658510
  }]
}
This is a synthetic customer fixture based on the approved feature shape, not a live response or provider test parameter.
What should the cache-absent fixture prove?
Omit the optional field according to the documented shape and assert live_pending_no_cache. Do not create a blank entity. Cobalt says a cache miss does not prove absence from the state registry.[4]
Complete that same request once with a live match and once in a separate case with final live no-match. This proves the absence branch does not predict the terminal outcome.
Add malformed-shape tests without inventing provider behavior. The customer parser should reject wrong types, missing required correlation for an incomplete response, duplicate conflicting fields, and payloads larger than approved limits. Preserve a safe diagnostic and keep the request out of decision-bearing paths. These tests prove defensive handling, not that Cobalt will send those forms.
How Should Age and Match Policy Be Tested?
Which timestamp boundaries belong in the matrix?
Test just below, exactly at, and just above each threshold; missing, null if permitted, malformed, seconds mistaken for milliseconds, future time, clock skew, and very old values. Retain raw and parsed timestamps and assert the named fallback.
Cobalt tells customers to use cached record timestamps for their own recency decisions[5] and notes state-level update variation.[6] The test runner should not assume one universal age.
Which matching cases should be included?
Test exact agreement, punctuation and suffix changes, stable-identifier agreement with name variance, stable-identifier conflict, different top candidate, missing optional match context, and query-input correction. Use Cobalt's matched-field guidance[7] and confidence guidance[8] only for documented context, not to invent one universal threshold.
Assert whether each case auto-resolves, waits for live, or opens neutral review under the customer's policy version.
Run policy tests with exact configuration snapshots. A boundary case is meaningful only when the threshold, unit, state scope, action, and precedence rule are known. Include duplicate and conflicting rules, missing defaults, expired rules, and rollback to a prior version. Fail closed when the resolver cannot select one authoritative policy.
How Should Asynchronous Delivery Be Tested?
Which polling and callback sequences matter?
Test repeated incomplete polls, cache present then final, cache absent then final, callback completion, polling completion, callback and poll racing, callback delayed after polling completion, and an incomplete event arriving after terminal state. Cobalt supports retry and callback patterns for long-running requests.[9]
Both transports must call one transition function and produce the same final state and effect count.
Which failures should be injected?
Crash before event-key reservation, after reservation, after observation storage, after state commit, after queue publish, inside the effect consumer, and before acknowledgment. Retry the same event after each failure.
AWS recommends retry backoff and idempotency so repeated operations converge on one state effect.[10] Assert database state, messages, tasks, final-decision calls, and visible history together.
Use production-like transaction isolation and at least two concurrent workers. A serial mock cannot expose a poll and callback both reading pending state before either commits. Delay one worker after it reserves an event key, crash another after effect publication, and confirm that retries converge without moving terminal state backward.
How Should Cached-Live Variance Be Tested?
What does an agreement case prove?
Return a live observation with the same stable identifiers and material fields. Assert that the live record becomes primary, cached history remains, prepared values are confirmed, and no duplicate review is created.
If a screenshot is included in the fixture, attach it only to the live observation. Cobalt notes that screenshots and official documents vary by state and lookup path.[11]
What does a variance case prove?
Change one material identifier, candidate, or status and assert neutral review, both immutable observations, field comparison, blocked final-only actions, and one structured disposition. Include a non-material punctuation case so the test distinguishes difference from material conflict.
Do not make the variance fixture a fraud result. Its purpose is to prove source-aware comparison and customer policy.
Test the review lifecycle through closure. Create the case once, show both observation versions, record a structured disposition, release only allowed downstream actions, repeat the final event, and attempt to close from a stale browser. Assert that the rationale names evidence and that no duplicate case or decision appears.
How Should Interfaces, Logs, and Exports Be Tested?
What should the reviewer see in each state?
Capture source, age, live-pending label, permitted actions, cache-absent message, live-complete label, variance view, artifact parentage, and final no-match state. Test stale browser sessions and server-side action rejection after live completion.
Export cached summaries and live artifacts. Verify that source and phase remain visible outside the application.
What should the trace contain and exclude?
Assert request and observation IDs, retryId, delivery path, timestamps, policy version, prior and next state, reason, action, idempotency result, and disposition. OWASP recommends logs that include event status, reason, and action.[12]
Assert that credentials, tokens, and unapproved payload data are absent from general logs. Verify authorized evidence access and controlled denial for unrelated roles.
Test clock semantics and ordering. Provider update time, customer receipt time, event commit sequence, and user-action time serve different purposes. Delay ingestion and skew a worker clock to confirm that state order comes from durable versions rather than sorting one timestamp. An invalid or future updatedAt must fail to the live path, not appear newly updated.
What Are the Release and Production Readback Gates?
Which automated checks must pass?
Require contract tests, state-transition tests, policy boundaries, concurrency and failure injection, interface assertions, security checks, export provenance, observability, and regression coverage. Run them with the exact policy and schema version intended for release.
Keep an expected event trace for each core scenario. A pass means state, effects, visible labels, and audit records all agree, not merely that an endpoint returned 200.
Require evidence from every layer: request fixture, adapter output, persisted observations, transition record, queued and consumed effects, interface snapshot or assertion, and audit events. Store the test run ID across them. This makes a failure diagnosable and prevents a passing unit test from masking an incorrect downstream label.
Which real readback should follow deployment?
Verify one authorized production or production-like happy path with valid input, then read back the request, interim state if observed, final state, observation links, effect count, logs, and visible interface. Do not claim the feature works end to end from a server start or structural response alone.
If a real request completes too quickly to expose the interim branch, that run can verify the terminal path but not the new branch. Use supported environments and customer-controlled mocks for deterministic branch coverage, and keep the completion claim scoped. Do not claim a live cachedData happy path until one has actually been observed or provided through an authorized fixture route.
Monitor illegal transitions, duplicate effects, unresolved pending requests, parse errors, and review volume. The asynchronous webhook guide covers delivery design, and the verification waterfall guide covers provenance. To review the matrix against your stack, schedule a demo.
Set rollback criteria before release. A rise in illegal transitions, unexplained observation loss, repeated final effects, or source-label errors should disable interim actions while preserving the ordinary live path. Keep the diagnostic records and repair plan, then rerun the same gate before re-enabling the feature.
Record the release decision, test run identity, known limits, and rollback owner beside the final gate result.